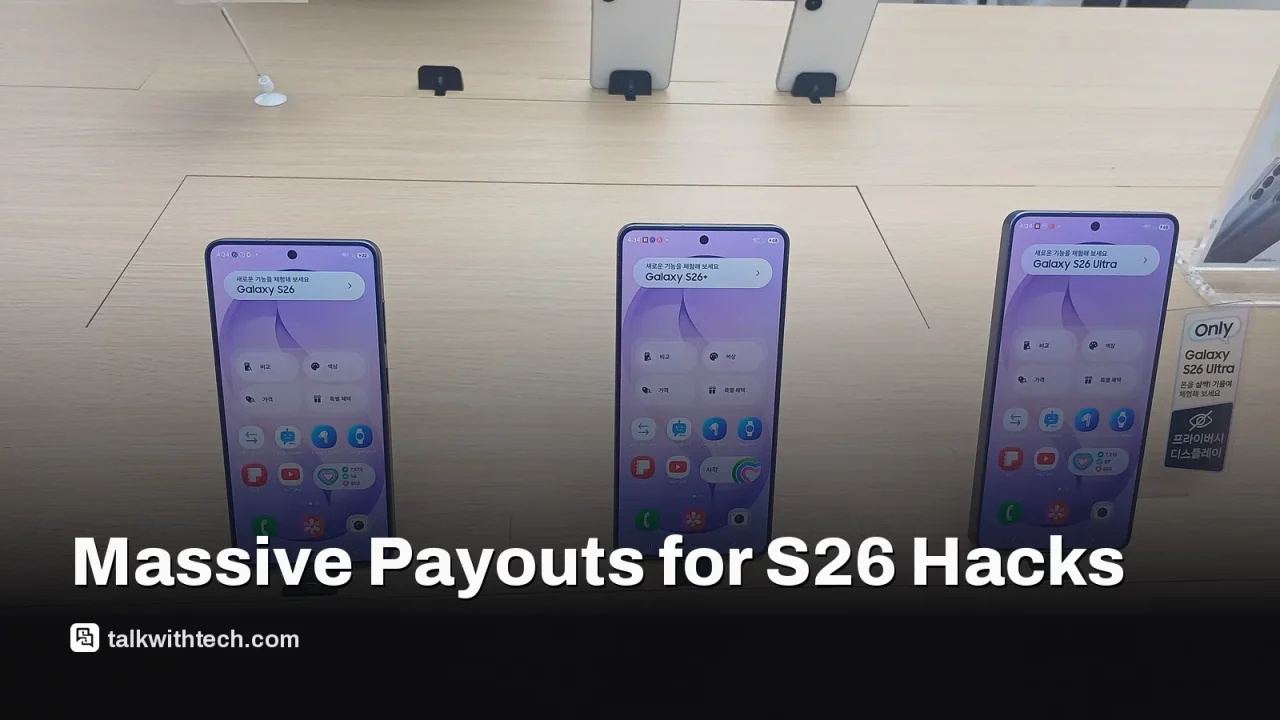
At Pwn2Own Ireland 2026, the Galaxy S26 was hacked in three separate demos, earning security researchers six-figure awards.
A total of 45 unique zero-day vulnerabilities were exploited across devices and categories.
The event underlines ongoing security risks in fully patched devices and the need for rapid vendor responses.
Quick read · 1 min
During Pwn2Own Ireland 2026, security researchers hacked the Samsung Galaxy S26 three times, earning a share of cash awards totaling over $232,500. The event showcased 45 zero-day exploits across seven categories, underscoring ongoing security challenges even on up-to-date devices.
What it means for you: keep devices updated, enable automatic updates, and practice good security hygiene. Vendors typically patch flaws in the weeks after disclosure.
What happens next: patches will roll out in the following weeks; monitor your device’s security notices and apply updates promptly.
The Galaxy S26 was hacked three times on the second day of Pwn2Own Ireland 2026, with researchers walking away with a share of $232,500 in cash awards. The Galaxy S26 was targeted by KAIST Hacking Lab’s Kyeongmin Kim, PetoWorks, and Mobile Hacking Lab’s Dimitrios Valsamaras and Ken Gannon. The demos came as part of a broader showcase where 45 unique zero-day vulnerabilities were exploited across seven product categories.
Zero-day exploits are flaws that vendors don’t yet have patched. In the competition, researchers must demonstrate arbitrary code execution on the target device while it runs the latest firmware. After disclosure, vendors typically have a window (often 90 days) to fix the vulnerability before it’s publicly disclosed by the organizers. That timing matters for real-world users who expect patches quickly after such findings surface.
Other notable moments from day two included a quick hack of a Sonos Era 300 by the RET2 Systems team and a separate AI infrastructure hack that netted a large payout for the Out of Bounds team. Home devices and AI systems remain attractive targets at Pwn2Own Ireland, reflecting the growing attack surface in connected homes and enterprise-grade AI tools.
01
What is Pwn2Own Ireland and why does it matter?
Pwn2Own Ireland is part of a global security contest where researchers try to break widely used consumer devices and software to reveal how attackers might exploit them. The goal is to uncover bugs before criminals do and push vendors to patch promptly. The competition covers phones, smart home devices, printers, and AI infrastructure, among other targets.
02
Which devices were hacked and how serious were the flaws?
The Galaxy S26 was among several devices targeted. The competition also saw attempts on the Google Pixel 10 and the Home Assistant Green smart home hub, among others. The hacks demonstrated across multiple categories suggest that even the latest devices can still be vulnerable in surprising ways, especially when complex chains of flaws are chained together to achieve full control.
03
What this means for ordinary users
For everyday users, the takeaway is simple: even premium devices with current firmware can have undisclosed flaws. No single hack means users should panic, but it does mean you should keep your devices up to date and install patches as soon as they’re released. It also highlights the importance of a layered security approach, regular OS updates, app updates, strong device passwords or biometrics, and cautious behavior with third-party apps and links.
04
What happens next
After Pwn2Own Ireland, vendors typically review the disclosed flaws and release patches over the following weeks. If you own a Galaxy S26, ensure you have automatic updates turned on so you don’t miss crucial security fixes. Researchers and vendors will continue to monitor and respond as new flaws surface in ongoing security efforts.
A UPS shipment carrying sensitive F-35 cockpit canopy and weapons-bay door components was allegedly rerouted through Hong Kong after an employee missed an ITAR alert, raising questions about secure handling of military tech.
Raheim Hamilton, co-creator of Empire Market, gets 40-year prison term for running a platform that facilitated hundreds of millions in illegal drug sales and other crimes.
3 min read
We use cookies to understand how readers use Talk With Tech, so we can make it better. Is that OK? Privacy policy
The Daily Brief
Today's biggest tech stories, in 5 minutes
Every morning, the news that matters from AI, phones, apps and the people shaping tech. Explained in plain English. Free.
One email a day. No spam, unsubscribe anytime. Privacy policy